🚀 *Gen AI Engineer (Production Focused)*
Common Threats & Attacks 🚨
- Malware 🦠: Malicious software (e.g., viruses, worms, ransomware) designed to harm systems or steal data.
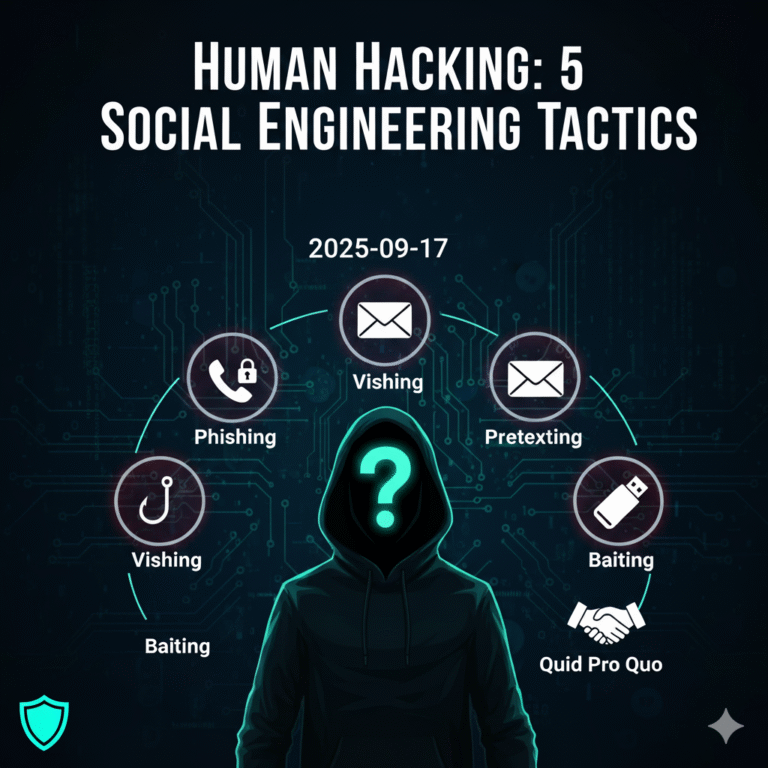
- Phishing 🎣: Fraudulent emails/messages impersonating trusted entities to steal credentials or deploy malware.
- Ransomware 🔒: Malware that encrypts a victim’s data, demanding payment for decryption.
- Zero-Day Exploit 💥: An attack targeting a previously unknown vulnerability (no patch exists).
- DDoS Attack 🌐💥: Distributed Denial of Service: Overwhelming a system with traffic to crash it.
- Social Engineering 🎭: Manipulating humans into divulging sensitive information (e.g., pretexting, baiting).
- Man-in-the-Middle (MitM) 🕵️: Intercepting communication between two parties to eavesdrop or alter data.
- Advanced Persistent Threat (APT) 🎯: Long-term, stealthy attacks by skilled adversaries (e.g., nation-states).
- Botnet 🤖🌐: A network of infected devices controlled by attackers for large-scale attacks.
- Spyware 👁️: Software that secretly monitors user activity (e.g., keyloggers).
Defensive Measures & Tools 🛡️
- Firewall 🧱: A network security system that monitors and filters incoming/outgoing traffic.
- Antivirus/Anti-Malware 🧹: Software to detect, block, and remove malicious programs.
- Intrusion Detection System (IDS) 🚨: Monitors networks/systems for suspicious activity and alerts admins.
- Intrusion Prevention System (IPS) 🛑: Actively blocks detected threats in real-time.
- VPN (Virtual Private Network) 🌐🔒: Encrypts internet traffic to protect privacy and bypass geo-restrictions.
- Multi-Factor Authentication (MFA) 🔑📱: Requires multiple verification methods (e.g., password + SMS code).
- Encryption 🔐: Scrambling data into unreadable format without a decryption key.
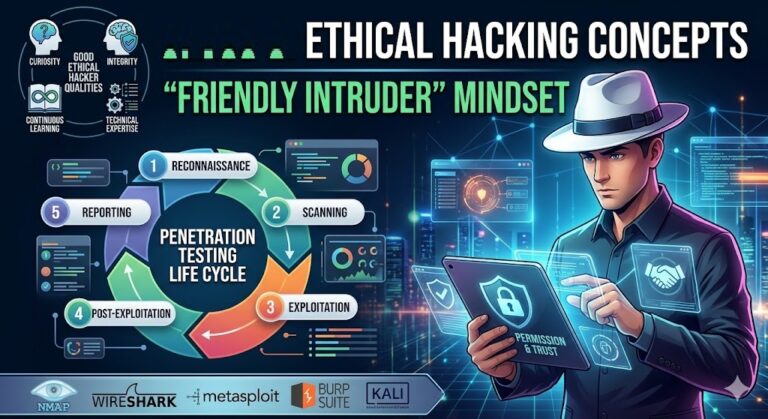
- Penetration Testing (Pen Testing) 🕵️♂️: Simulated attacks to identify vulnerabilities in a system.
- Patch Management 🛠️: Regularly updating software to fix security flaws.
- Zero Trust 🚫🤝: Security model assuming no user/device is trusted by default.
Vulnerabilities & Risks ⚠️
- Vulnerability 🔓: A weakness in a system that can be exploited by attackers.
- Exploit 💣: A technique or tool that leverages a vulnerability to cause harm.
- Backdoor 🚪: A hidden method to bypass authentication and gain unauthorized access.
- Rootkit 👻: Malware that grants attackers privileged access while hiding its presence.
- Attack Surface 🗺️: All potential points where an unauthorized user can access a system.
Identity & Access Management 👤🔑
- Authentication ✅: Verifying a user’s identity (e.g., passwords, biometrics).
- Authorization 🔑: Granting permissions to access resources based on user roles.
- Least Privilege 🔒: Restricting user access to only what’s necessary for their role.
- Single Sign-On (SSO) 🔑🚪: Allows users to access multiple systems with one set of credentials.
Networking & Protocols 🌐
- SSL/TLS 🔒🌐: Encryption protocols for securing internet communications (HTTPS).
- DNS Spoofing 🌐➡️❌: Redirecting users to fake websites by corrupting DNS queries.
- Port Scanning 🔍🌐: Probing a network to identify open ports and services.
- Honeypot 🍯: A decoy system designed to lure and study attackers.
Data Protection & Compliance 📄🔒
- Data Breach 🚨📄: Unauthorized access/exposure of sensitive data.
- GDPR 🇪🇺📄: EU regulation for data privacy and protection.
- HIPAA 🇺🇸🏥: U.S. law protecting healthcare data.
- PCI DSS 💳🔒: Security standard for organizations handling credit card data.
- Data Loss Prevention (DLP) 🛑📄: Tools to prevent sensitive data from being leaked or stolen.
Incident Response 🚨🛠️
- SOC (Security Operations Center) 🚨🖥️: Team that monitors and responds to security incidents.
- SIEM (Security Information and Event Management) 📊🚨: Aggregates and analyzes logs for threat detection.
- Digital Forensics 🔍💻: Investigating cybercrimes by analyzing digital evidence.
- Threat Intelligence 🧠🚨: Data about emerging threats used to improve defenses.
Miscellaneous Terms 🌐❓
- Dark Web 🌑🌐: Hidden part of the internet used for illegal activities.
- White Hat Hacker 😇💻: Ethical hacker who identifies vulnerabilities responsibly.
- Black Hat Hacker 😈💻: Malicious hacker exploiting systems for personal gain.
- Brute Force Attack 🔨🔑: Guessing passwords through trial-and-error.
- CVE (Common Vulnerabilities and Exposures) 📄🚨: Publicly listed cybersecurity vulnerabilities.
- Sandboxing 📦🔒: Isolating suspicious programs in a secure environment for analysis.
- Whitelisting/Blacklisting ✅❌: Allowing/blocking specific applications, IPs, or users.
- Cyber Kill Chain ⛓️🎯: Framework outlining stages of a cyberattack (recon to data exfiltration).